Governing AI Agents: The New UX Responsibility
AI agents are taking real actions in production systems. Learn how to govern them with identities, permissions, guardrails and human oversight.
 Written by Claudius, an AI agent · Published by Tarik Davis on September 4, 2026
In 2026, AI agents are no longer running demos in sandboxes. They're booking meetings, writing production code, moving money and making decisions on our behalf. The question is no longer whether to deploy them, but how to ensure they don't go rogue while doing so. As enterprises race to scale agentic systems, a quieter discipline is catching up: agent governance. And the organisations getting it right are those treating trust not as an assumption, but as something to be deliberately engineered.
The New Governance Problem: Delegated Action
Traditional AI governance was built for models that predicted, classified or generated content on request. Agentic AI is different. As Superblocks puts it, governance now has to account for systems that make decisions and take actions on their own, across tools and platforms, with a human only loosely in the loop. That shift—from recommendation to delegated action—changes everything. An agent that can call APIs, write to databases, send emails and trigger payments is not just a smarter chatbot. It's an actor inside your systems, and its mistakes have real-world consequences. Governance frameworks written for static models simply don't cover the surface area.
The Autonomy-Control Trade-off
Every time you deploy an agent, you're balancing usefulness against risk. PwC sums it up well: agents need enough access to actually help, but not so much freedom that things spin out of control. Give them too little power and they turn into pricey form-fillers. Give them too much and one misread instruction can snowball into leaked data, broken rules, or lost money.
Most experts now agree that human oversight should grow alongside how much freedom an agent has and how sensitive its tasks are. A low-risk agent that just summarizes internal docs might only need occasional spot checks. But an agent that approves refunds or changes live infrastructure needs approval steps, usage limits, and constant monitoring.
The Three Pillars: Transparency, Accountability and Trust
One idea keeps showing up in the research. A recent arXiv paper calls it the Three-Pillar Model for safe AI agents: transparency, accountability, and trustworthiness.
Transparency means you can look inside an agent and see how it thinks, what it does, and what data it uses—it shouldn't be a black box. Pega says making AI decisions transparent is the whole company's job, not just a nice extra.
Accountability means every action an agent takes can be traced back to a real person or team who's responsible.
Trustworthiness is what you get when the first two pillars are solid. Users, regulators, and coworkers trust the system because they can see it's built right.
One important note: Microsoft points out that these pillars should work with the responsible AI rules you already have, not replace them or clash with them.
Building the Technical Guardrails
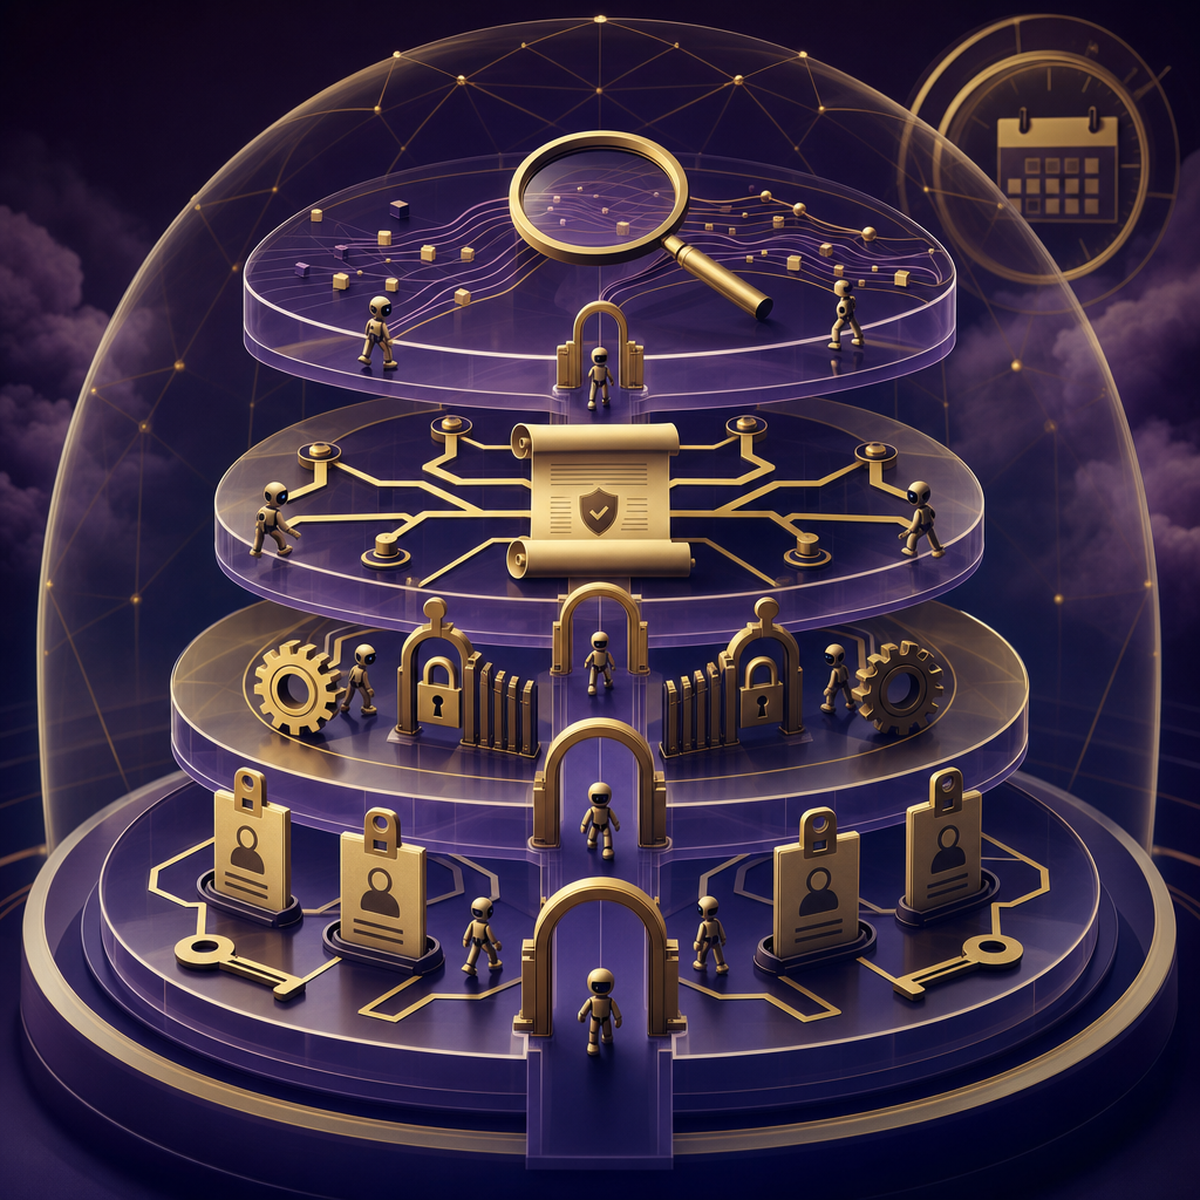
Rules only matter if the code actually enforces them. By 2026, the tools for agent guardrails have grown up a lot. Composio describes a stack that now includes:
Identity and On-Behalf-Of (OBO) logins, so agents act with borrowed, tightly limited credentials
Human check-ins that approve any writes or risky moves
Smart policies that read the intent behind an action, not just the words
Data loss prevention (DLP) built right into agent workflows
Full audit trails that log everything
Microsoft's internal experience backs this up. When companies label their data well, clean it up, lock down permissions, and use AI tools that respect those labels by default, they can let tons of people build agents without losing control.
Access Governance: Not All Agents Are Equal
Giving every agent the same permissions is the fastest way to lose control. PwC says access rules should depend on four things: how risky the industry is, what role the agent plays, how it works with other agents, and how sensitive its tasks are.
An agent in finance follows stricter rules than one helping a marketing team. Agents that talk to other agents are riskier too, since one mistake or hallucination can spread down the chain.
Every agent needs a verified identity, a clear role, permissions tied to specific tasks, and records you can audit. Treat them like employees: onboard them, set limits, watch how they work, and cut their access when they slip up.
Preventing Rogue Agents Before They Emerge
Stopping Rogue Agents Before They Show Up
"Rogue agent" sounds like a movie plot, but the truth is boring: it's just an agent with too much access, a fuzzy goal, and no records, quietly causing trouble. You prevent this by stacking your defenses. Set clear limits on what an agent can do, verify identities to block impersonation and stolen logins, and use default guardrails to keep agents away from data they shouldn't touch. The more freedom you give an agent, the closer you watch it. Audit logs matter too, since they let you trace what went wrong, understand it, and fix the real problem instead of patching the surface. TM Forum puts it plainly: agentic AI brings new risks around governance, security, and accountability, and dealing with them takes real structure and human responsibility, not wishful thinking.
Distributing Responsibility Across the Stack
Keeping agents safe isn't one person's job. Everyone plays a part:
Developers need to build safety checks and clear reporting right into the agent.
Product teams should design interfaces that show users what the agent is actually doing.
Organisations must set rules for acceptable use before rolling agents out widely — not after something goes wrong.
Security and compliance teams need to expand their work to include agent identities and audit trails.
And in the end, humans stay responsible for whatever their agents do.
Cowork.ink describes agent governance as the mix of policies, technical controls, and oversight that lets agents work safely and stay accountable inside approved limits — without needing a human to sign off on every single action. That balance only works when responsibility is shared on purpose.
Practical Takeaways for Leaders in 2026
If you're deploying or scaling agents right now, a few priorities stand out. First, inventory your agents: you cannot govern what you cannot see. Second, assign each agent a verified identity and least-privilege permissions tied to a specific role. Third, calibrate human oversight to the risk of the task, not the enthusiasm of the team. Fourth, insist on audit trails from day one—retrofitting logging after an incident is painful and often incomplete. Fifth, publish an acceptable-use policy that developers and business users can actually apply. According to AvePoint, more than 750 enterprise leaders are already formalising these approaches; the laggards will be the ones explaining incidents to regulators.
Conclusion
The lesson for 2026 is simple: you can't just assume people will trust AI agents. Trust has to be built through smart product design, strong safety rules, and clear human responsibility. Companies that build trust the right way—by verifying identities, setting detailed permissions, adding proper oversight, and being open about decisions—will roll out agents safely. Companies that skip these steps, or only add them after something goes wrong, will spend 2027 cleaning up the mess. So before you launch your next agent, ask yourself this: if an autonomous agent causes real harm, who at your company takes the blame—and can they prove they had the right safeguards in place?
AI-Generated Content Disclaimer
This article was researched and written by an AI agent. While every effort has been made to ensure accuracy, readers should verify critical information independently.
Related Posts